The 'only install applications from a trusted source' mantra no longer holds true, as supply chain attacks bypass malware detection solutions and practices.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
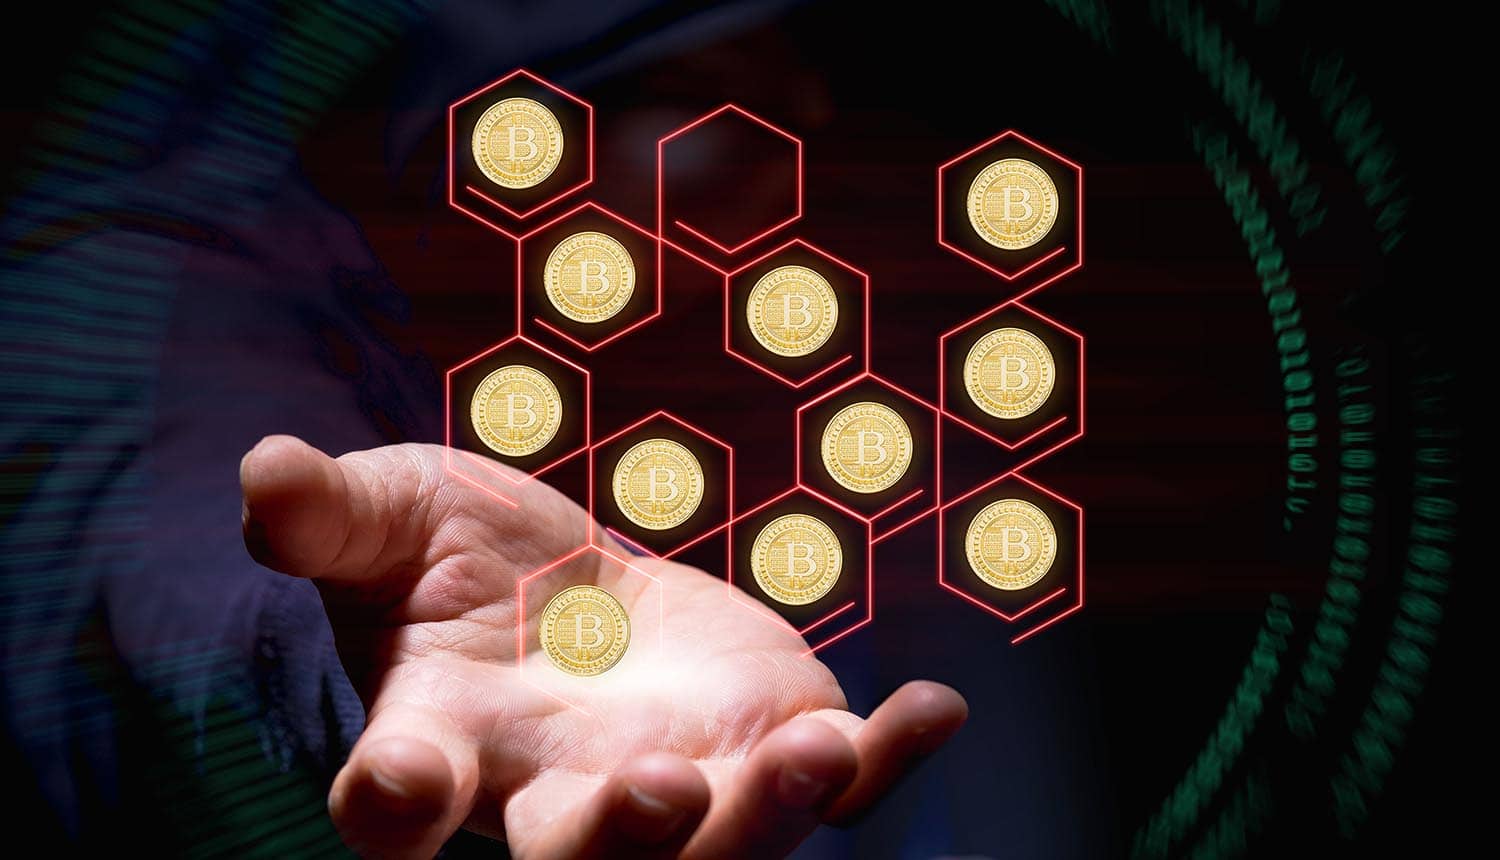
Hackers donated thousands of dollars in stolen Bitcoins to various charitable causes. While it's unclear what the true motives are, the donations will almost certainly be forfeit.
A recent survey by the SANS Research Program showed 58% of respondents identified IT compromises as a leading initial attack vector for ICS/OT incidents. This reflects the increasingly interconnected nature of IT and OT environments and highlights the risks associated with this convergence.
Security leaders often assume patching failures stem from technical limitations. In reality, many of the most disruptive patching delays originate from coordination breakdowns across teams, tools, and timelines.
Preloaded apps on current Lenovo, HP and Dell systems are found to have unique and serious security vulnerabilities that require end users to take extra steps to fix.
In military parlance, the phrase “when the balloon goes up” refers to the moment when hostilities with an adversary are imminent. The Chinese spy balloon that sailed over the continental United States signifies something different: a vast—and increasingly brazen—penetration of American networks and communications systems.
Many IoT devices can easily be hijacked, weaponized and made part of IoT botnets to launch DDoS attacks, it’s called the DDoS of Things.
EEA’s PSD2 regulation aims to protect consumers against fraud by securing the digital payments for Card Not Present (CNP) transactions. Study shows that merchants have seen some higher loss from failed and abandoned transactions than that from fraudsters.
Implementing MFA methods improves an organization's security posture by lowering the likelihood of identity theft, as a hacker would require more than just the user's password to obtain access to their account.
Which? report says old routers supplied by UK internet providers Vodafone, Virgin, Sky, EE, and others put millions of internet users at security risk of cyber attacks.