The new CSC report warns that national cyber defense is "stalling" in most areas and "slipping" in some. Its central point of criticism is that only 35% of 82 recommendations that the commission made in 2020 have been fully implemented, with about 13% still facing barriers to progress and another 18% making progress but still distant from actual implementation.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
Second ransomware attack on Toll Group in three months shows lightning can strike twice, and there's no grace period that's honored before the next attack.
Broadband Provider Brightspeed has experienced a data breach that exposed over 1 million customers, with hackers threatening to disconnect home internet customers.
The CFAA case of Van Buren v. U.S. has concluded with a decision resulting in a clarification of how crimes involving "authorized access" are defined.
A Canvas hack has leaked nearly 280 million records from faculty, staff, and students across 8,809 colleges, online learning platforms, and school districts.
A third-party data breach at the online DIY platform ManoMano has affected nearly 38 million customers after attackers breached its subcontractor’s Zendesk instance.
Online businesses must prioritize credential stuffing mitigations by detecting and preventing automation in credential stuffing, and identifying compromised credentials of legitimate users and forcing them to change password to disincentivize the attackers and break the attack lifecycle.
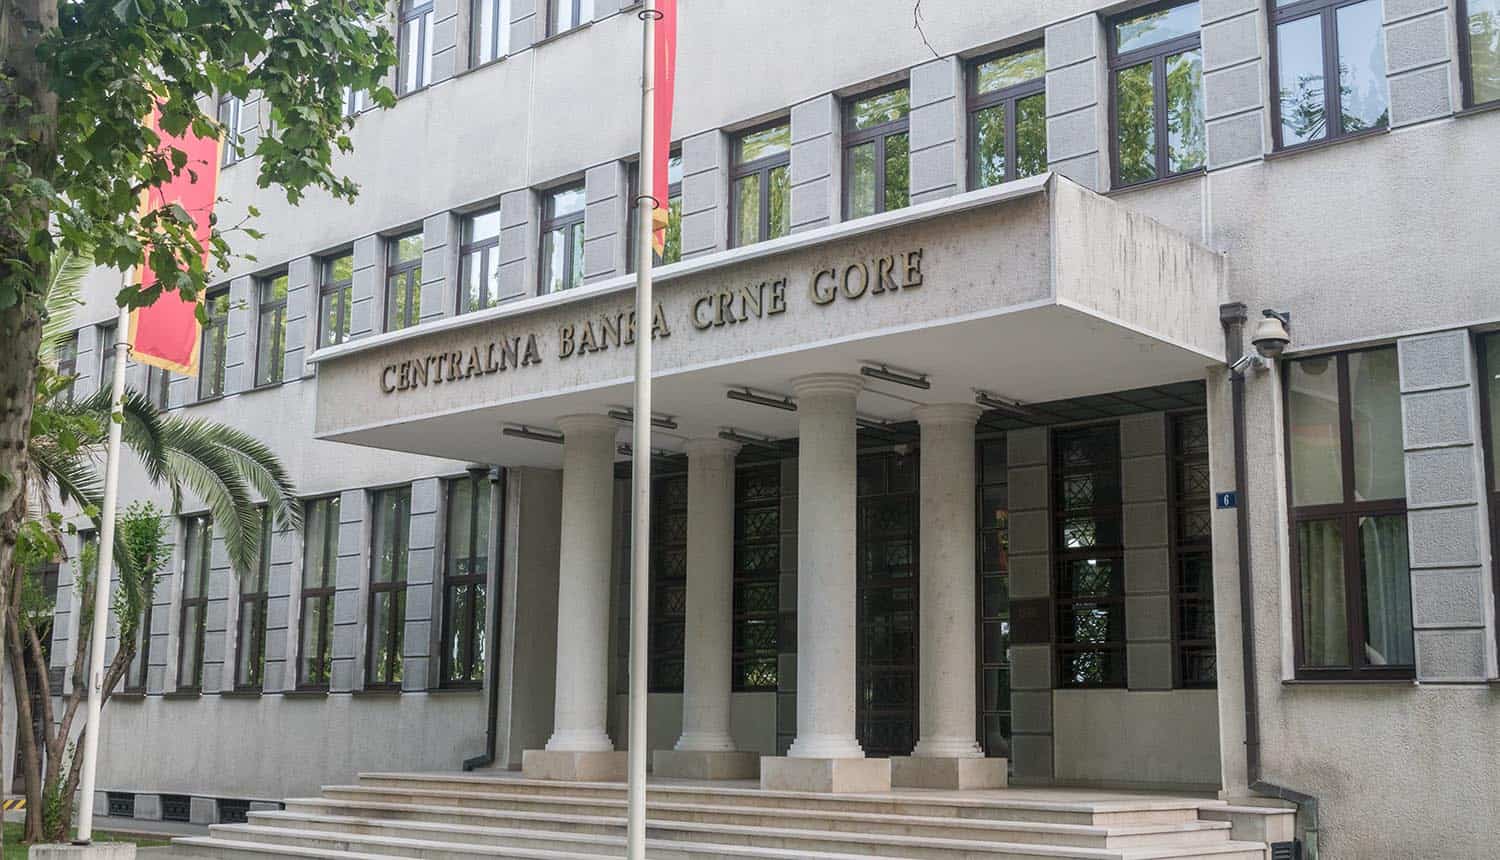
Montenegro is dealing with a brutal ongoing campaign of ransomware attacks that appears to be coming from criminal groups in Russia. Government agencies in Chile have also been hit by a new form of ransomware that targets Linux servers.
A Japanese government official disclosed a data leak that exposed Olympics ticket buyers' account credentials but the Olympics organizers denied being the source of the breach.
A botnet used by a state-backed Chinese hacking group has lost at least some of its capacity, according to security officials that spoke to Reuters anonymously. The Volt Typhoon group has been targeting US critical infrastructure since at least mid-2021.