A new Russia-based family of malware has been observed using a large language model (LLM) to issue commands on compromised systems in real time, which can potentially improve attacker capability by allowing them to shift tactics during an attack without having to introduce new payloads.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
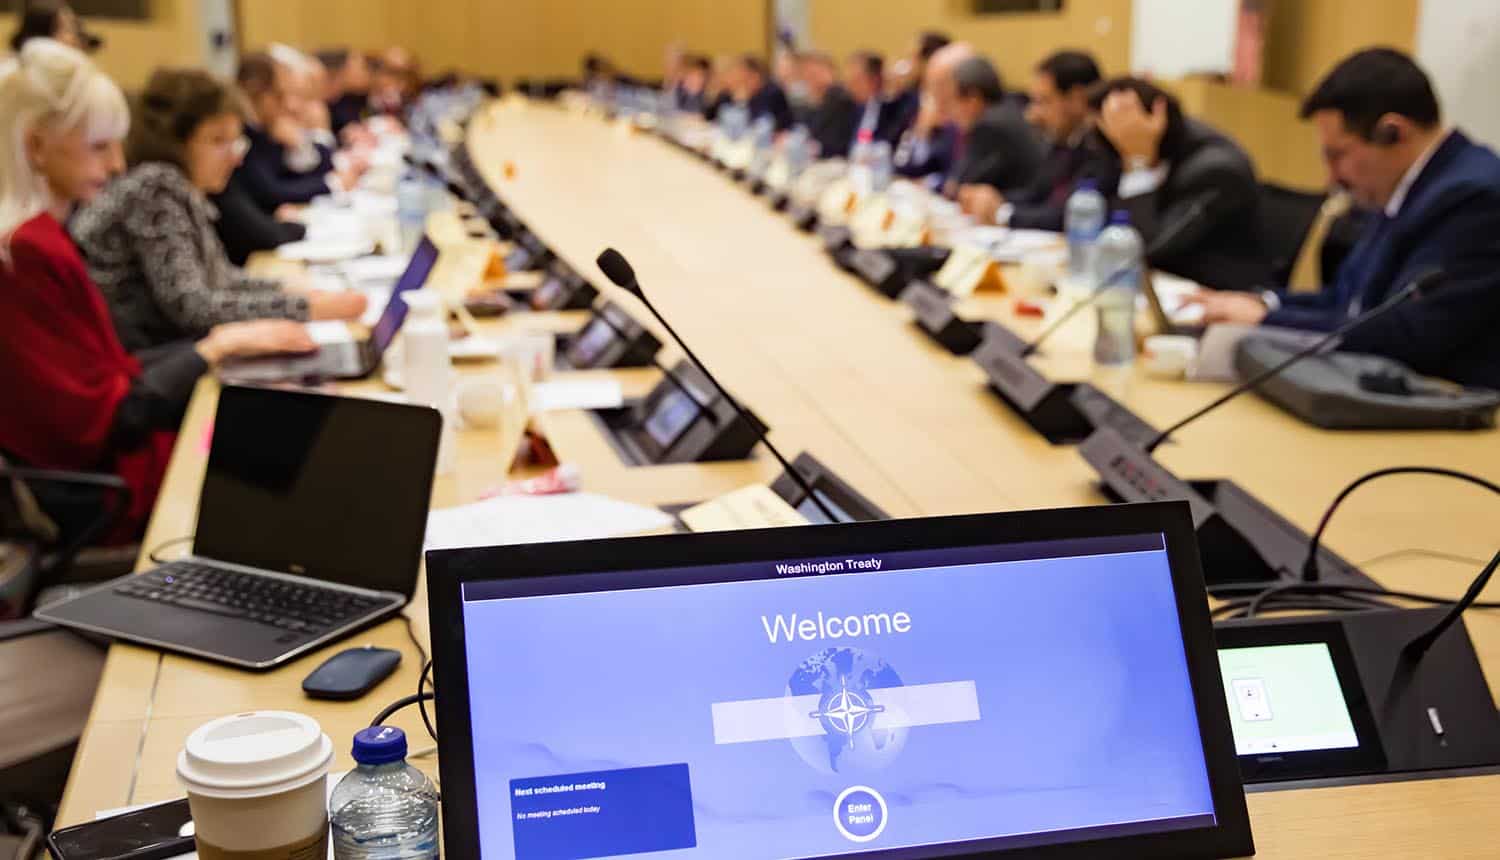
Hundreds of NATO documents of "extreme gravity" were reportedly stolen and made available on the dark web, and the Portuguese government is facing tough questions about why the breach was not discovered for weeks.
Joint international law enforcement effort involving about a dozen countries has taken down Ragnar Locker ransomware gang's dark web site, with an announcement that at least one arrest had been made.
The BlackByte ransomware gang's "2.0" reboot of their data leak site sports a new "feature" for its victims: a tiered payment system that allows for smaller payments to delay publication of sensitive data, or to simply download and recover it prior to having it dumped for public viewing.
AI deepfakes were used to contact three foreign ministers, a US Governor, and a member of Congress around the middle of June via the Signal messaging app. Two of the officials received fake voicemail messages mocked up to use Rubio's voice, and another received an invite to join a chat.
WeWork, a co-working company which operates in world's biggest cities, was reported running a WiFi security breach since 2015. Companies’ information was exposed to anyone who has local network password in the office.
South Korea's National Police Agency has revealed that state-sponsored North Korean hackers have been waging an all-out espionage campaign against the country's defense companies since at least 2022, and have lurked in the networks of some targets for over a year.
One overlooked aspect of continuous testing is its potential for the automation of security checks. By utilizing the automated power of continuous penetration testing, a company would no longer need to waste the precious time of their employees.
For IT and security teams, the dramatic increase in demand for applications and digital services, coupled with these heightened expectations for flawless application performance, creates a huge challenge.
EFF and Lookout traced Dark Caracal to Lebanon and has infected Android users in more than 20 countries and stolen hundreds of gigabbytes of dat. Cyber espionage using fake apps with Android malware is the new trend as nation states and cybercriminals move towards using mobile as the target platform.