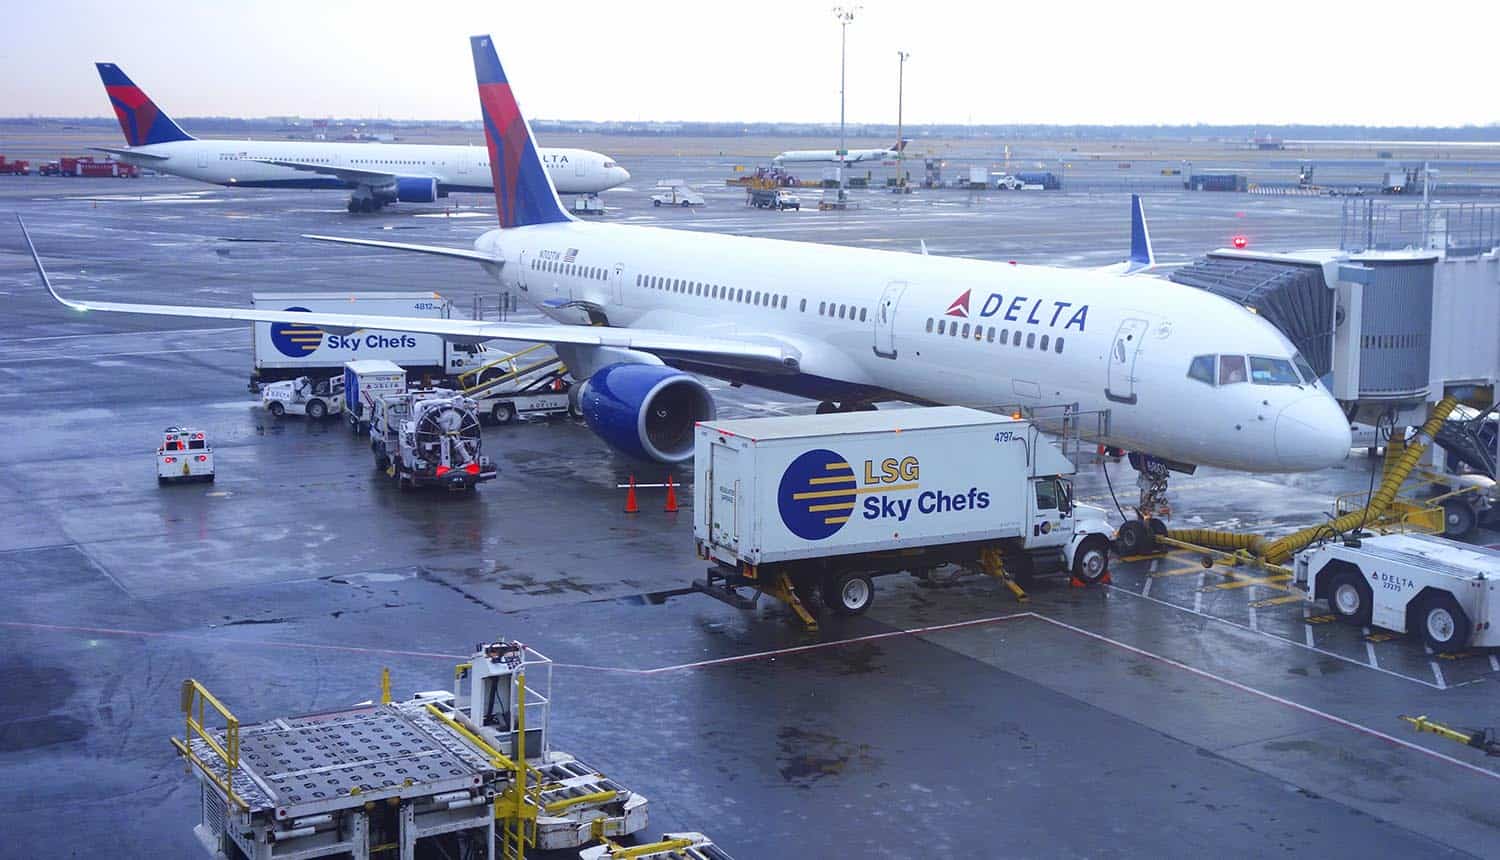
As early as late July, Delta CEO Ed Bastian was threatening CrowdStrike with a lawsuit to recoup some of its estimated $500 million in losses from flight disruptions. CrowdStrike has filed its own suit pointing to Delta's slow recovery from the IT outage.
CRA has lost about $190 million in payments made to scammers since 2020, with the highlight item being a $40 million tax refunds scam in which the perpetrator simply logged into an account and requested the astounding sum of money using false T4A income reporting slips.
Insurance administrator Landmark Admin confirms that the May 2024 data breach stemming from a ransomware attack leaked the personal information of over 800,000 individuals.
What the new AI guidance boils down to is essentially the legal principle that it cannot be considered "reasonable" respect for or protection of privacy to enter personal information into an AI system, unless that AI has been expressly designed for this.
The Biden White House continues to seek a balance between AI innovation and safe ethical use with a new national security memorandum that stresses the need to outcompete rivals, but also sets limits in the most potentially abusive areas.
The U.S. state of Georgia’s election website experienced a “probing” cyber attack from a suspected nation-state threat actor, delaying absentee ballot requests.
The noyb privacy complaint notes that Pinterest has invoked the "legitimate interest" exception to user consent for ad tracking, one of a small handful of such exceptions provided for by the GDPR. The problem for the company is that Meta has already tried this tack and failed.
UnitedHealth Group (UHG) has confirmed that the February 2024 Change Healthcare data breach leaked the sensitive personal information of 100 million people, making it the worst healthcare leak in history.
Each of the fined companies learned that they had been breached during the SolarWinds hack in 2020 or 2021. Each was found by the SEC to have negligently minimized its cybersecurity disclosures in ways that could mislead investors, but all using somewhat different language.