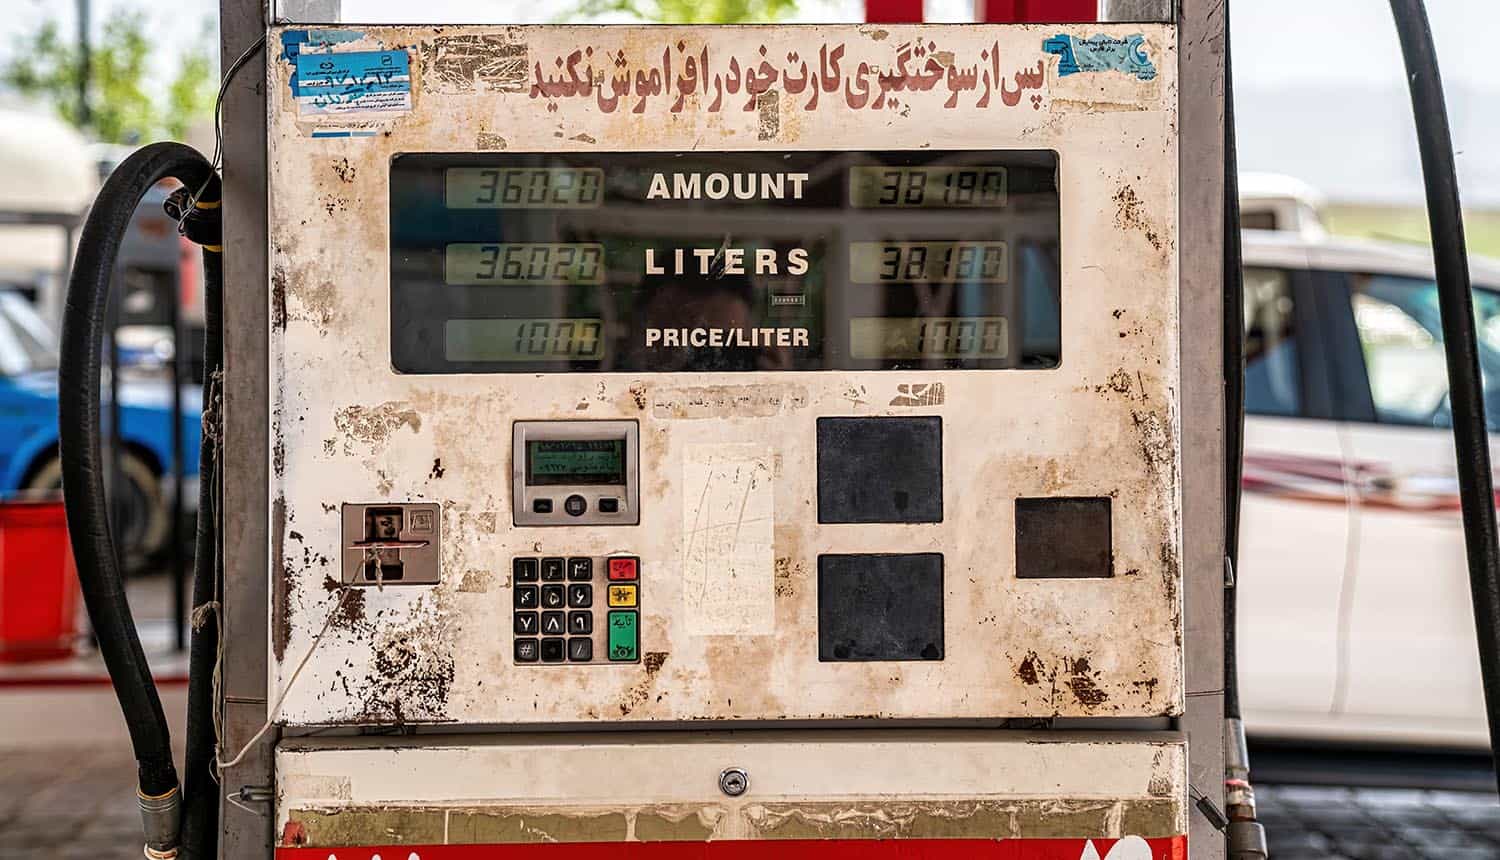
Cyber attack disrupted Iran’s gas stations accepting government-issued smart cards for subsidized fuel while hacked electronic signs mocked Supreme leader Khamenei and demanded gasoline.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
A group of hackers widely believed to be supported by Iran's government breached a personal email account belonging to FBI director Kash Patel, which contained material dating from 2010 to 2019. The hackers claimed this was in retaliation for recent FBI operations against them.
As part of a major change in strategy, it now appears that Iranian hackers APT33 are shifting their focus to critical infrastructure targets, threatening ICS security.
Iranian hackers Cyber Av3ngers breached a water utility in Aliquippa, Pennsylvania, by targeting an Israeli-made SCADA system they consider a legitimate target.
Mysterious organization exposed tools and source code used by Iranian hackers, including personal information of some Iranian Ministry of Intelligence members responsible for state-sponsored cyber attacks.
A phishing campaign by state-sponsored Iranian hackers has targeted over 100 government entities and other organizations with version 4 of the Phoenix malware backdoor.
Iranian hackers are extending their attacks to political, diplomatic and military targets in U.S, Australia, and U.K. It now appears to be part of a long-term, state-sponsored cyber hacking campaign by Iran.
The United States Department of Justice (DOJ) has indicted three Iranian hackers for a campaign of attacks dating back to 2020, including critical infrastructure companies and government agencies.
Two Iranian hackers have been indicted for election interference, charged with stealing information from state voter rolls to personally target thousands of individual voters as well as members of Congress and campaign staffers.
Iranian hackers installed crypto miner on federal agency’s network after exploiting unpatched Log4Shell vulnerability on the VMWare Horizon server to gain access. The threat actors moved laterally to the domain controller, compromised credentials and implanted reverse proxies on several hosts to maintain persistence.