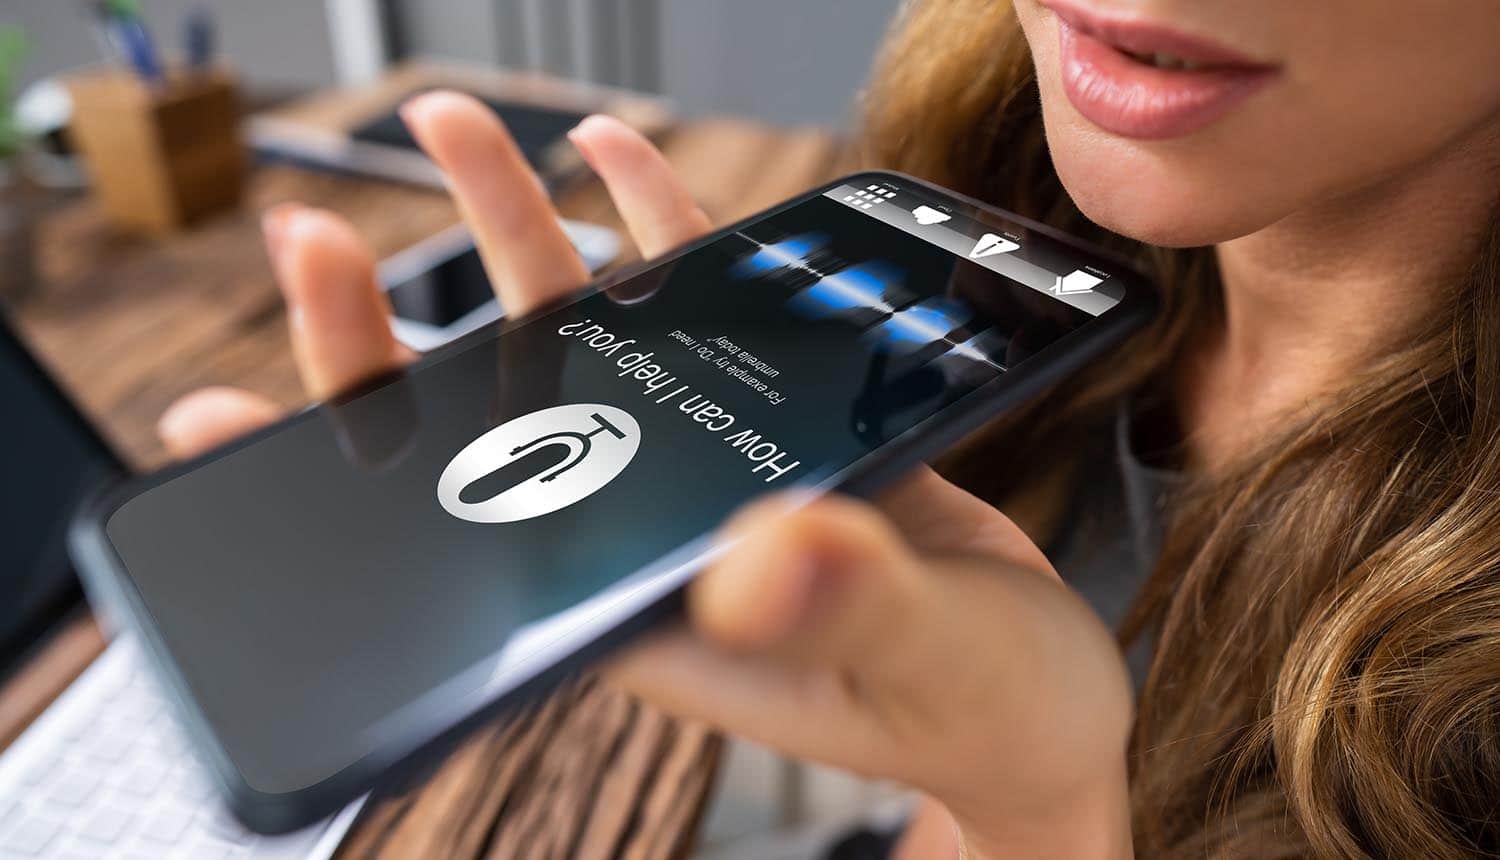
New type of attack on voice assistants uses ultrasonic waves to access the devices through solid surfaces that are inaudible to humans without the use of special equipment.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
Voicemail Phishing Attacks Threatens 100,000 Inboxes, Leaving Remote Workers Particularly Vulnerable
100,000 inboxes of remote workers have recently fallen victim to voicemail phishing attacks that could successfully bypass secure email gateways and DMARC authentication protocol.
New research shows that voluntary disclosures about cybersecurity risk can help mitigate the “contagion effect” that often impacts companies in an industry that has just been the victim of a major cyber breach.
Volvo disclosed a security breach that resulted in a R&D data theft by Snatch cyber threat actors. The company added that customers’ car safety and private information were not affected.
Israeli voter data was exposed by the country’s election management site that leaked admin credentials via an unprotected API endpoint in the homepage source code.
Recent DEFCON Voting Village report showed that some of the most popular and widely used voting machines vulnerable to hacking and that their security in the upcoming election is anything but assured.
Many have turned to VPN services to protect their privacy. However, the 2018 high-profile hack which NordVPN only acknowledged recently has raised questions on just how safe they really are.
A supposed data breach prompted coverage from a number of national media sources, as it claimed to involve popular social platform VRChat and some 2.5 million of its users. The fake notice went so far as to make up an accompanying fake disclosure statement from VRChat themselves.
The Vulkan Files revealed insight into Russian cyberwar plans and strategies and that company engineers work directly for Russian military and intelligence outfits and train state-backed hackers, run disinformation campaigns and provide support for cyber attacks.
More than 32,000 new Common Vulnerabilities and Exposures (CVEs) have been recorded so far this year alone, and the National Vulnerability Database (NVD), the US government repository for reported vulnerabilities, now faces an unprecedented backlog of CVEs.