Realizing the growing danger that insider attacks pose to businesses and national security, National Insider Threat Awareness Month has become an annual call for organizations to take preventative actions in an effort to minimize their risk of attacks.
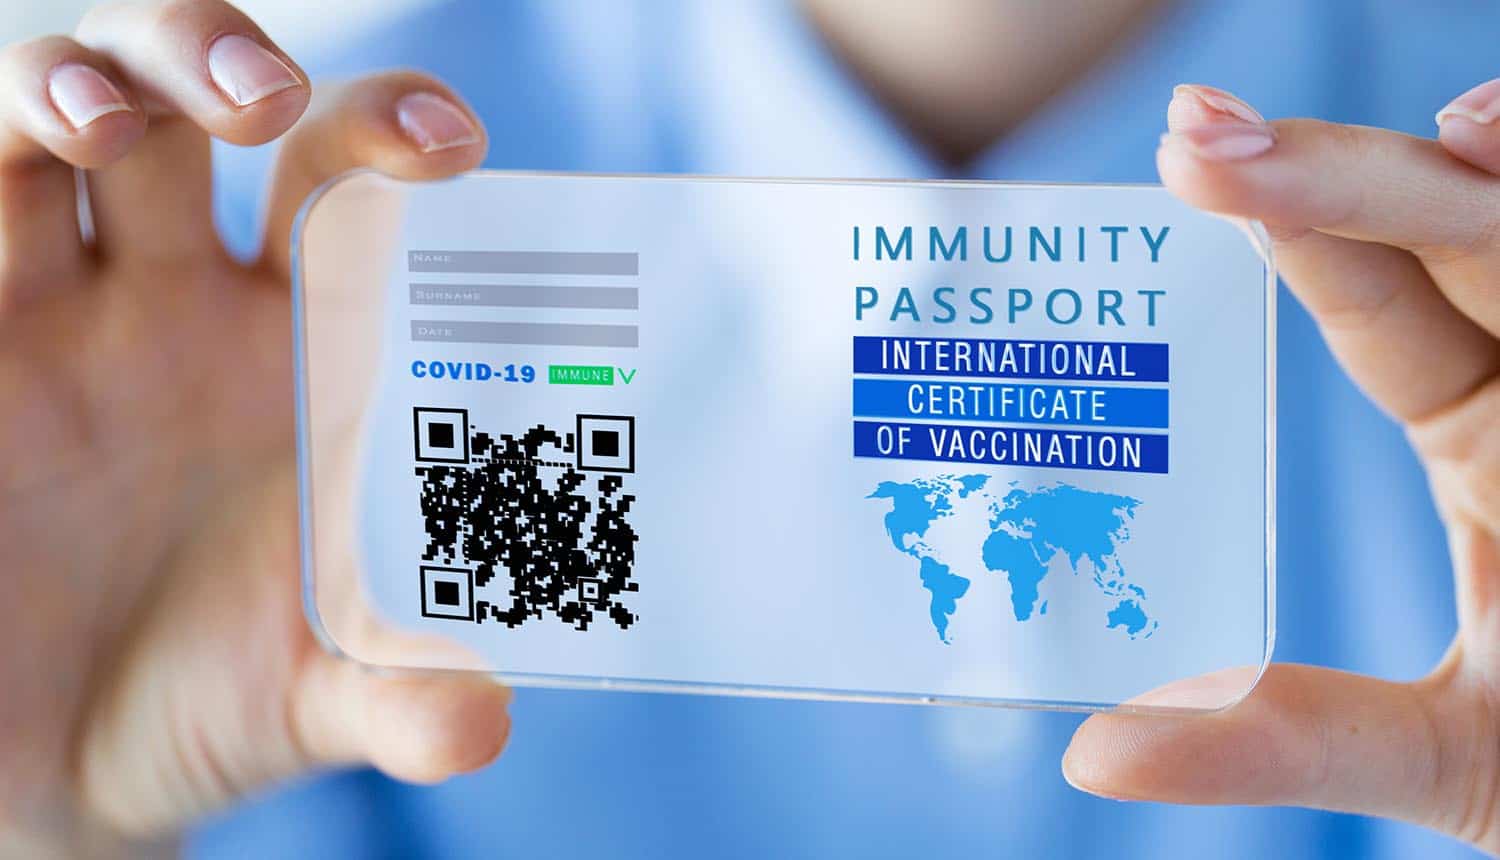
Countries are looking at vaccine passports as the ‘door opener’ for a return to normalcy. At the same time, threat actors know too well that taking advantage of the current pandemic has been a very lucrative over the last 18 months.
Many businesses are still struggling to understand and comply with data protection laws and regulations. Study finds that 62.4% of companies are still not ‘completely compliant’ with data regulations which means vulnerable consumers.
A trusted cybersecurity advisor is the gateway to a security-first mindset within a business -- you just need to know where to start and what to look for before engaging with such services.
How can well-intentioned companies avoid employing dark patterns by mistake? And how can privacy professionals, particularly attorneys, effectively counsel their clients away from this common, yet all too prevalent, practice?
Today's cybersecurity teams can’t get ahead of hackers because they’re drowning in data, fatigued by alerts, and dissatisfied with their jobs. Data elitism is the root cause of this negative environment, but companies can take steps to offset it.
President Biden’s Executive Order includes a provision that would require software vendors selling to the federal government to maintain a Software Bill of Materials (SBOM). Unfortunately, it’s not that simple.
In today’s digital privacy landscape, healthcare providers need to select an endpoint management solution that will allow their end-users to safely work with proprietary patient information without the risk of a data leak.
With much of the focus on cybersecurity practices, however, organizations are often overlooking their physical security needs. What are the common cyber-physical security threats to enterprises?
To reduce Total Cost of Fraud (TOCF), organizations must take a more holistic approach that considers the hidden costs of fraud to help minimize the cumulative financial impact and deliver better ROI for your fraud prevention efforts.