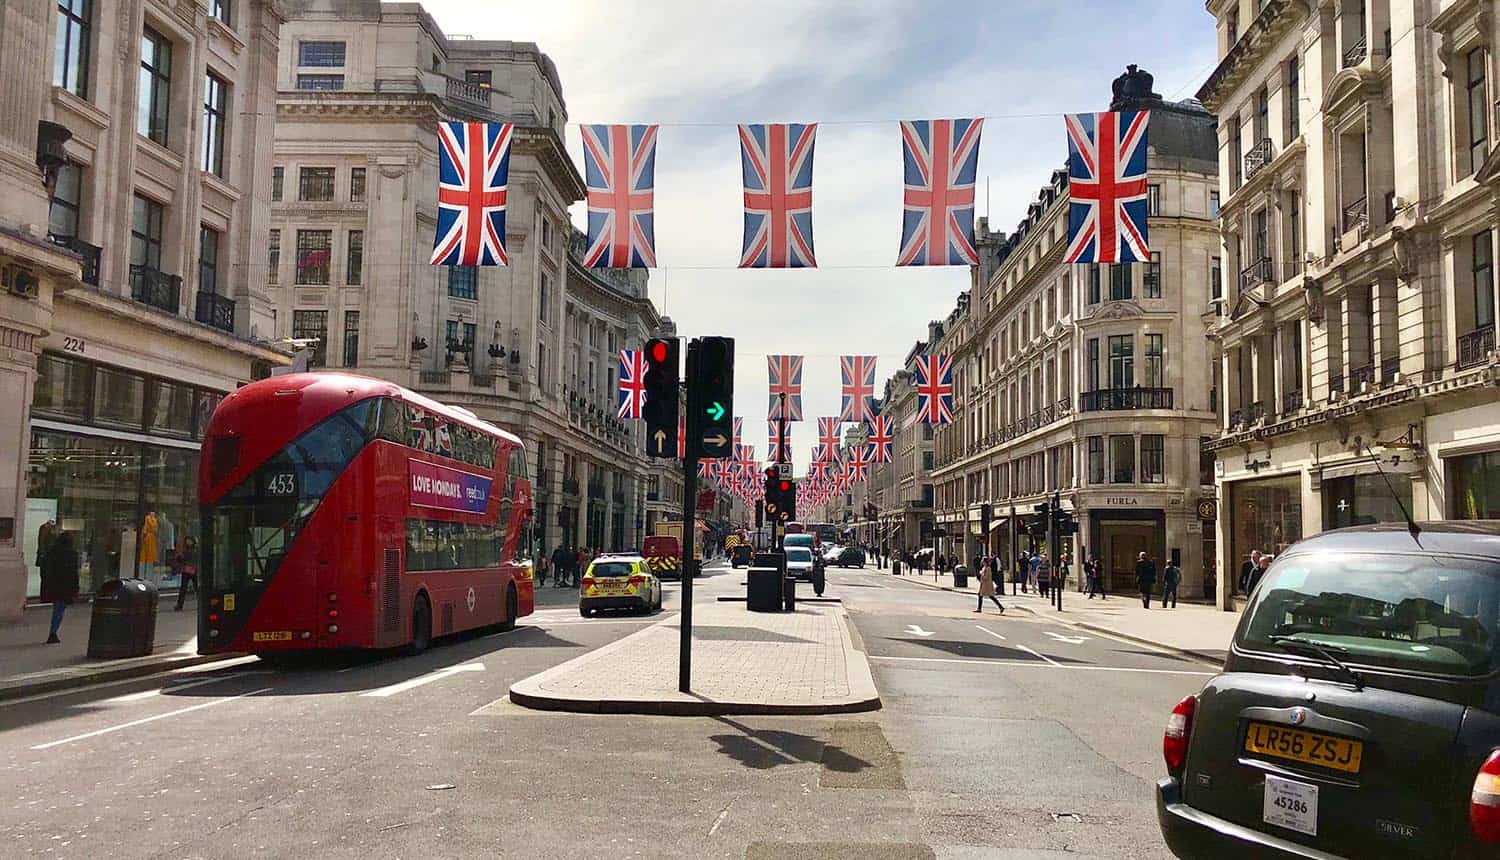
Transport for London (TfL) is responding to a cyber attack that affected its crucial IT systems, disrupting Dial-a-Ride and other services and forcing staff to work from home.
Cyber Security
Cyber criminals, state-sponsored hackers and even the occasional disgruntled employee are constantly looking to gain unauthorized access for a variety of purposes: theft of money, cyber espionage, personal information for sale or for use in scams, and damage to critical infrastructure for just a few of the most common.
So how does an organization mitigate an entire world full of continual cyber attacks? Just as buildings have a number of necessary elements of physical security: access control, cameras, alarms and so on; there are similar key elements of cyber security that are absolutely vital for just about any modern business.
It starts with identifying and closing the most common doors that attackers use. For example, phishing attacks on employees are far and away the most common initial point of entry. The breach of even a low-level employee account can quickly turn into an escalation in access privileges and the ability to reach sensitive information. This is also true of smart devices, which are generally more poorly secured than computers and phones.
The Trump Cyber Strategy is broken into six policy pillars meant to guide development of more specific measures and their future implementation. Each of these outlines consists of only one to two paragraphs without a large amount of specifics, making it a shorter and somewhat vaguer document than similar cyber policies laid out by prior administrations.
NSA and CISA issues joint report warning of cyber threats from state-sponsored actors targeting critical infrastructure, directing owners and operators to take immediate actions.
Security researchers have documented a Facebook credential phishing campaign that has been active since late 2021, and has been highly successful in duping victims using an authentic-looking spoofed login page.
Artificial intelligence (AI) has rapidly emerged as the double-edged sword of the cyber threat environment. Sophisticated AI models now serve as both potent tools for attackers and vulnerable hinge points for organizations girding against intrusions.
Emerging cyber risk quantification methods are allowing boards to ask “what if” questions if operating conditions change, and to align cyber risk with what they know about the business—upcoming economic challenges, potential merger and acquisition activities, or even the effect on the company’s financial statements or stock price.
Defending organizations utilize AI-powered email security measures to enhance network protection, detect advanced malware and ransomware, optimize critical data center processes, improve threat response times, and reduce human error. Unfortunately, threat actors have also identified the benefits of AI technology.
Cisco Talos recently highlighted the existence of 74 Facebook cybercrime groups with over 385,000 members. A growing concern that Facebook has become a platform to conduct cybercrime activities in plain sight.
The new “agentjacking” attack takes almost no real hacking ability to pull off. It's predicated on pulling a public credential that can readily be found in a web site's JavaScript source code, which can be used by anyone to get Sentry to accept an error event full of malicious instructions that is passed on to AI coding agents.
The long-running Qakbot malware botnet was disrupted by international law enforcement action in August, but its operators appear to still have some capability and are continuing to run spam email campaigns that attempt to pass ransomware.