China recently passed an encryption law to regulate encryption in public and private sectors, and also set forth guidelines for how cryptography should be used to help safeguard national security.
Chinese actors are deploying thousands of LLM gateways to clone U.S. frontier models, share credentials, and bypass geographic restrictions, rate limits, and usage metering.
The DeepSeek-V3 chat platform temporarily suspended new registrations in response to the cyber attack. The Chinese AI company grabbed headlines in January when assorted benchmark tests put it on par with the leading generative AI apps.
An attempt by major Chinese tech firms to circumvent Apple's new app tracking rules appears to have been shuttered. Apple sent a clear message to developers in the Chinese apps market that there would be no exemptions from its global rules.
Trend Micro finds the Chinese APT group has compromised at least 70 government organizations over the last two years, in 23 different countries. But the group's logs indicate it has targeted over 110 organizations in 10 additional nations.
Chinese APT group Weaver Ant breached and maintained a foothold on a large Asian telco network for four years using compromised Zyxel CPE routers for cyber espionage.
Tiandy, one of the largest firms in the video surveillance field, has a relationship with Iran. It is known for its ethically questionable product line, which includes "smart tables" designed to accompany Chinese torture chairs.
FBI's testimony suggests that the Chinese cyber threat to national security is becoming much more sophisticated in the realm of cyber espionage including abuse of the “Thousand Talents” program.
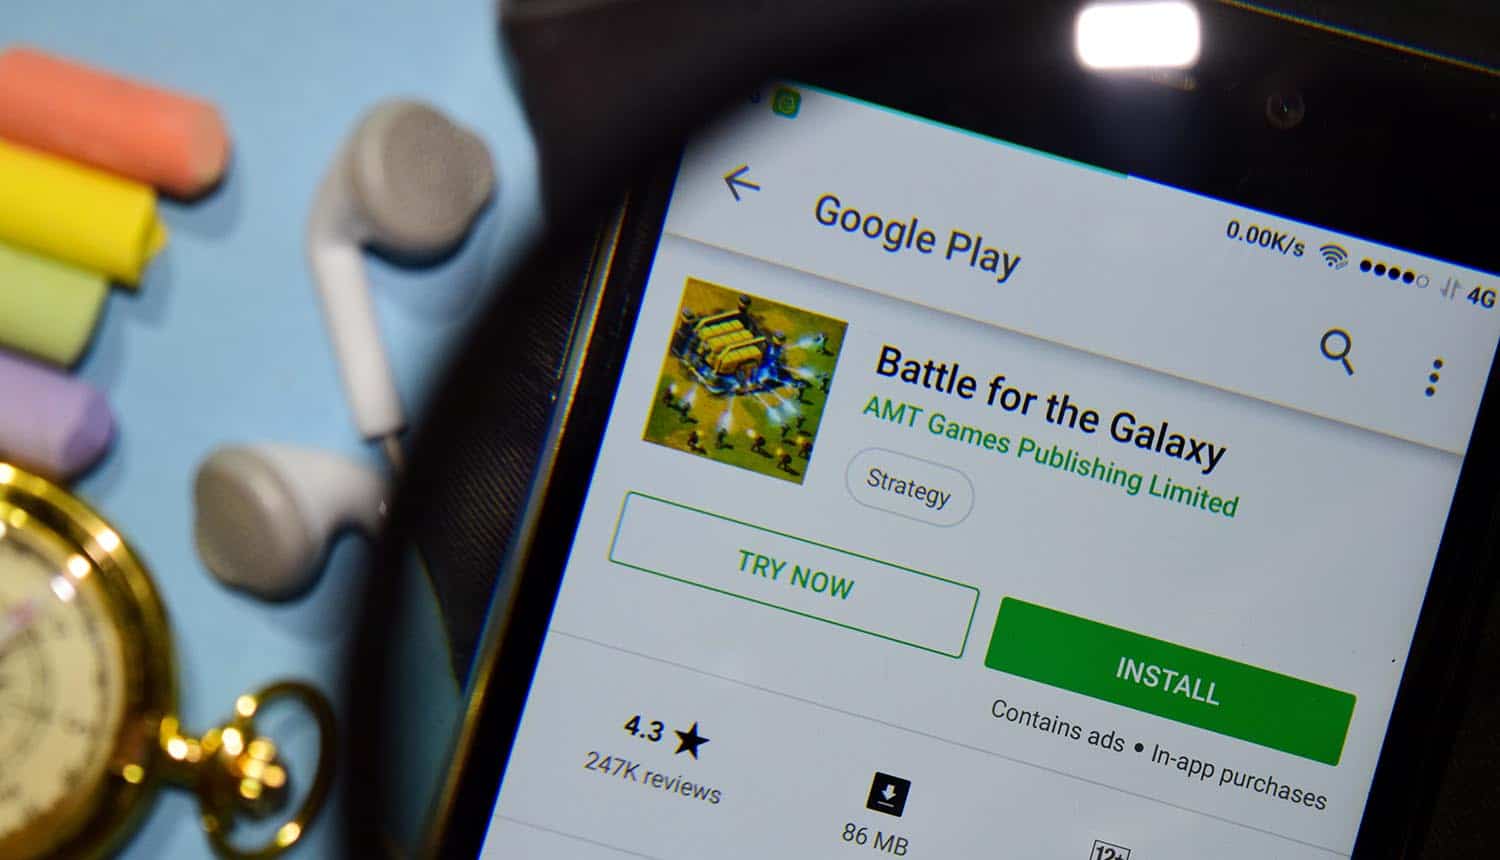
China-based game developer exposed personal information and transaction records of nearly 6 million Battle for the Galaxy players in an unsecured ElasticSearch data leak.
After one year of reviewing data collection practices on smartphone apps, the Chinese government imposed new regulations on 41 apps that were found to be out of compliance.